The challenge
AI in security is either useless or dangerous: an assistant that invents a rule ID or blocks an innocent address is worse than none. Automatic response built on a single rule can look fine in a demo and fail against a real attack.
An open-source security operations center that detects and responds to attacks, with an AI analyst that takes no action without human approval.
AI in security is either useless or dangerous: an assistant that invents a rule ID or blocks an innocent address is worse than none. Automatic response built on a single rule can look fine in a demo and fail against a real attack.
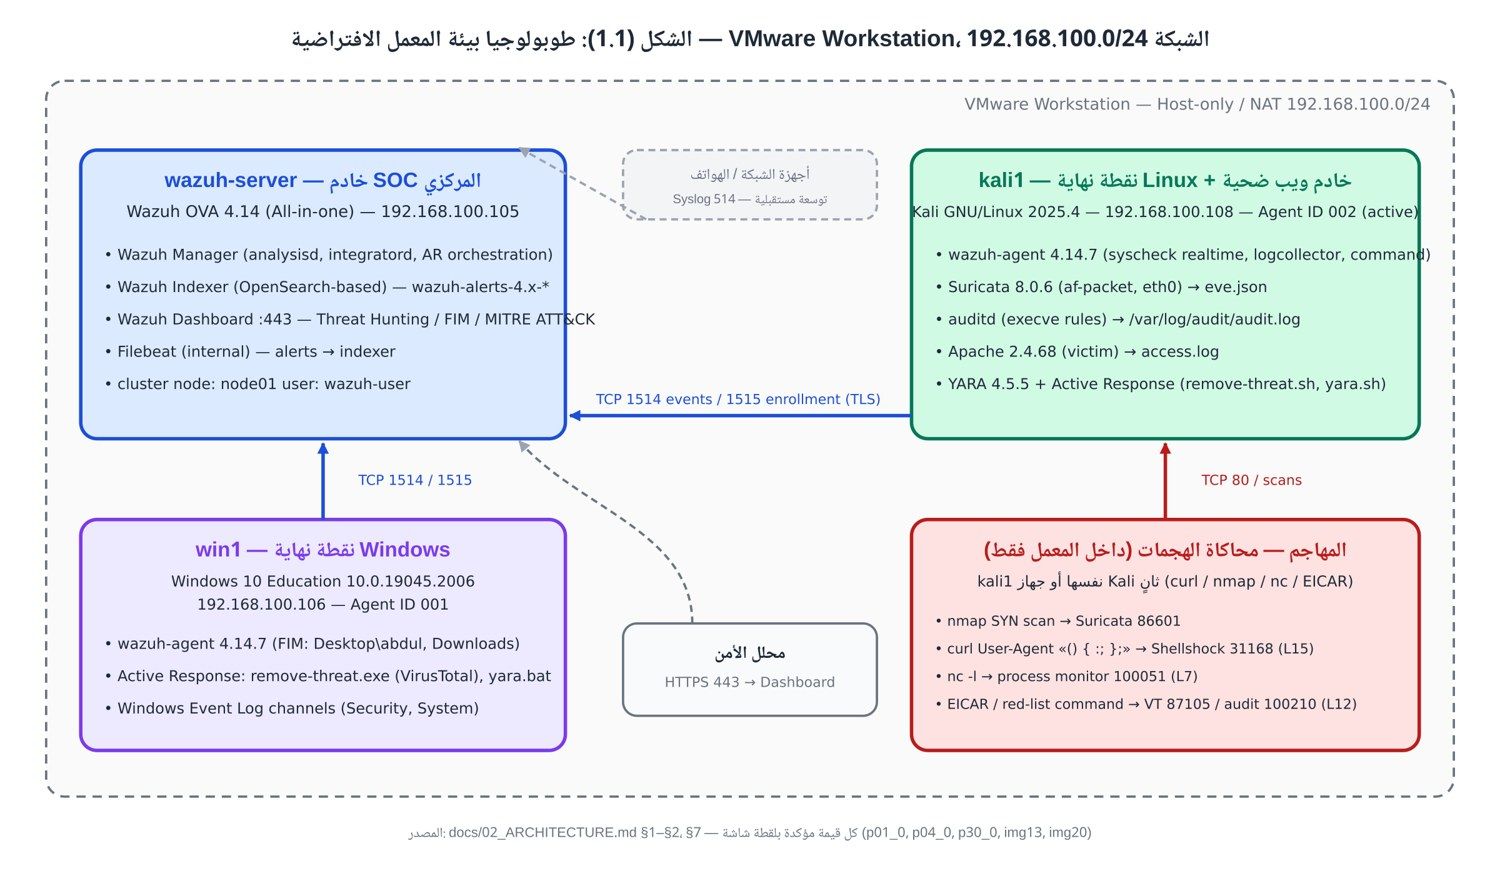
We built the center on open-source monitoring for network, files and endpoints, with documented use cases tested against real attacks in a lab.
We built the AI analyst on one rule: it ranks and filters from a fixed list of actions only, execution requires human approval, protected addresses are never touched, and every action is written to an audit log.
We reviewed the blocking rules against real logs rather than the plan, found a common attack that was getting through unblocked, and fixed it.
A center that detects the attack, proposes the action and blocks the attacker within moments of approval, with a full audit trail.
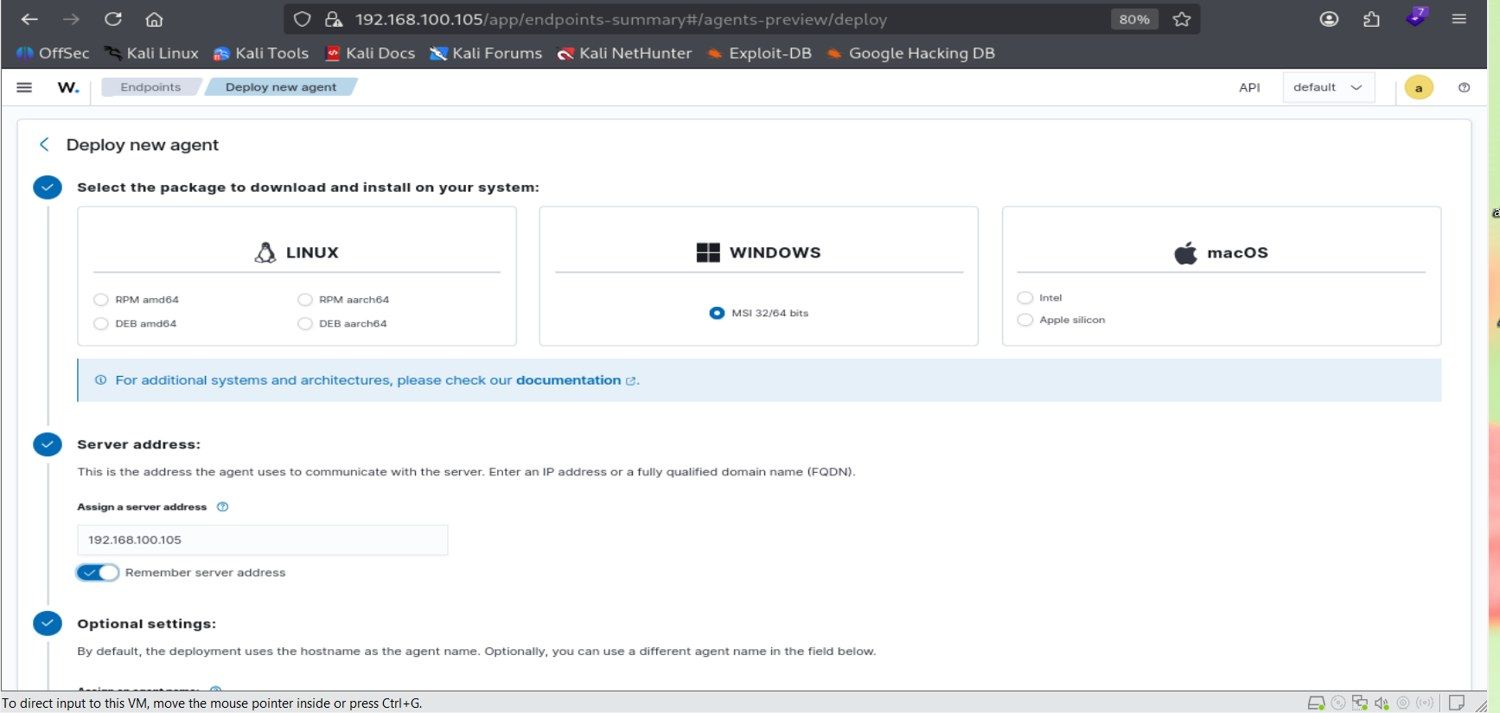
Screens are taken from the systems themselves, not mock-ups.
Tell us what you need in two lines and we will reply with the next step.
Tell us what you need in two lines and we will reply with the next step.
Message us on WhatsApp